Secure Email for Dental Practices: What to Check Before Sending PHI
“Secure email” is not a label you can verify from the inbox logo. For a dental practice, it is a combination of the service agreement, the functions covered by that agreement, account configuration, message handling, and staff habits.
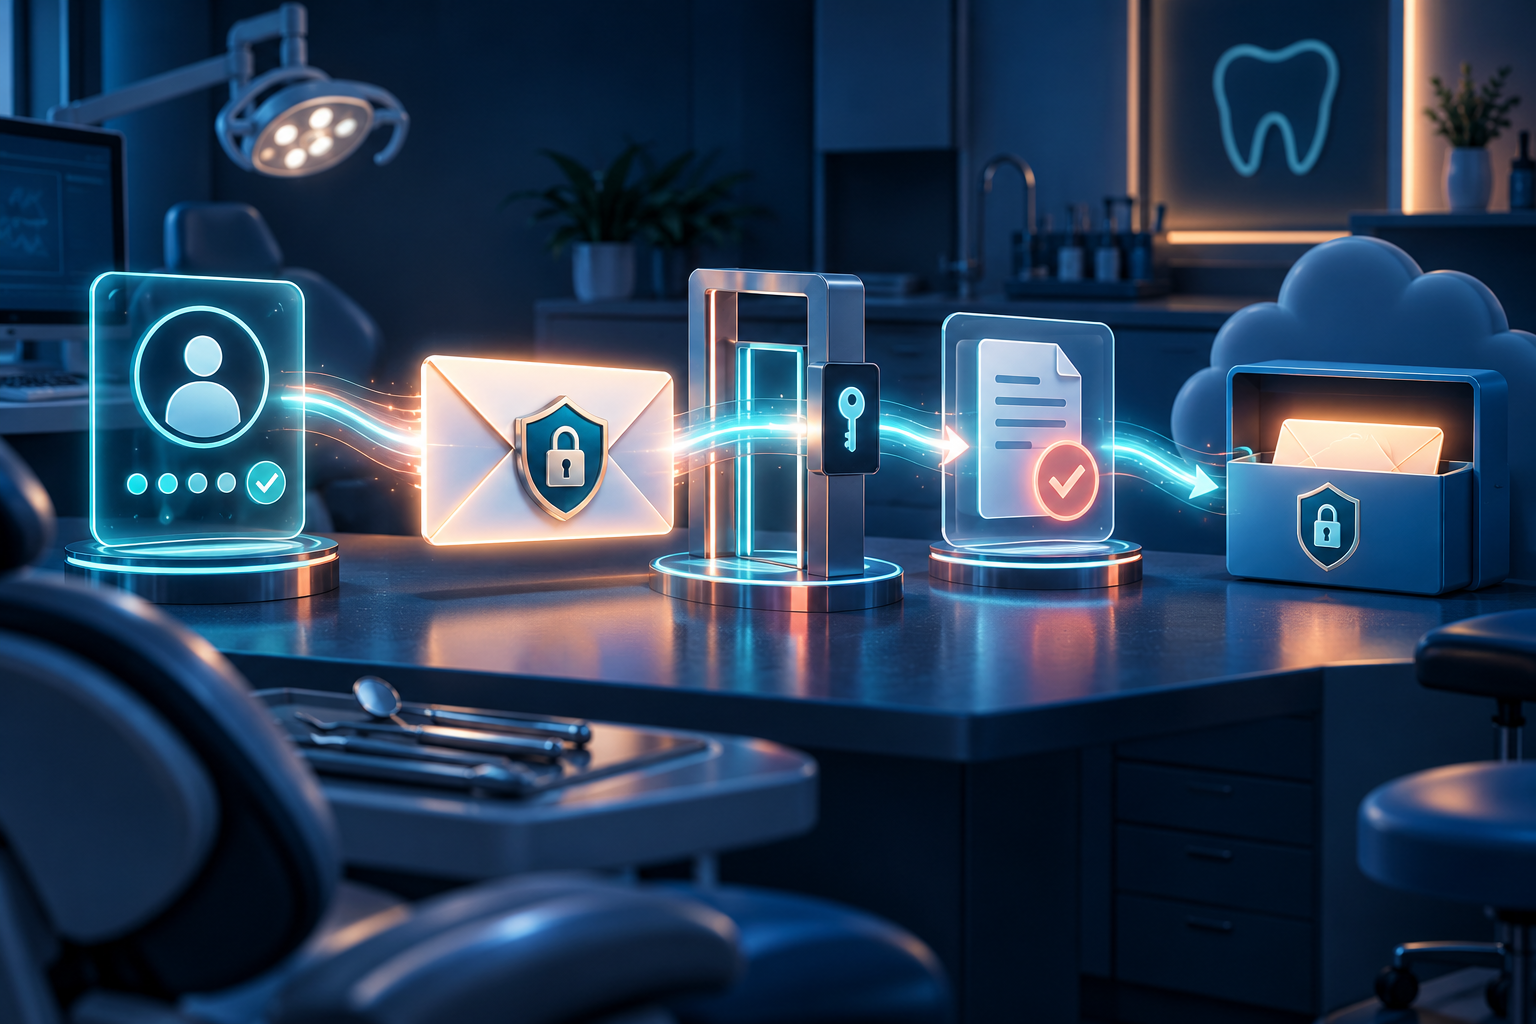
Before your team sends patient or insurance information, ask five questions: Who owns the account? Who can sign in? What service and functions are covered? How are messages and attachments protected? What happens when a message leaves the practice?
Start with the business account, not a personal inbox
A practice-managed account gives the office control over access, offboarding, recovery, and policy. A personal consumer account does not become suitable for routine PHI merely because it uses a familiar brand or a custom signature.
Google’s current Workspace guidance illustrates the distinction. Organizations subject to HIPAA must accept Google’s Business Associate Amendment before using PHI in listed covered services, and the organization remains responsible for deciding how it uses and configures those services. 1
The same buying question applies to any provider: identify the exact business service, plan, covered functions, connected apps, and agreement. Do not assume that every product sold by the same company is covered in the same way.
Understand what a BAA does—and what it does not do
A business associate agreement, or BAA, sets permitted uses and disclosures of PHI and requires the business associate to safeguard that information. HHS explains that these contracts clarify and limit how a business associate may handle PHI. 2
A BAA is necessary in many vendor relationships, but it is not a certification of the practice, the mailbox, or every connected feature. It does not choose safe settings, remove former employees, prevent a message from going to the wrong recipient, or review a third-party add-on.
Ask your provider or IT partner to show:
- the agreement that applies to your account;
- the services and functions included in its scope;
- any functions or add-ons that fall outside it;
- the settings your practice must configure;
- the person who owns ongoing review.
Check access before checking encryption
Message protection matters, but an inbox is still exposed if access is weak. Use named practice accounts, give each person only the access needed for the job, and remove access promptly when roles change.
Khamir’s practical recommendation is to turn information-security policy into repeatable daily habits: use multi-factor authentication, strong unique credentials, approved credential storage, screen locking, and practice-managed communication channels. 3
On a shared workstation, ask how the browser profile, password manager, screen lock, and account session are protected. A blanket ban on saved passwords is not the goal; an approved password manager can support strong, unique credentials. The goal is to keep work credentials out of personal profiles and unprotected shared sessions.
Review the whole sending path
HHS permits providers to communicate with patients by email when they apply reasonable safeguards, including checking addresses and limiting unintended disclosure. The Security Rule still applies to electronic PHI. 4
Have your IT partner demonstrate the actual path for both a message and an attachment:
- How does an authorized staff member sign in?
- What protection applies while the message moves and while it is stored?
- What does an outside recipient experience?
- What happens when the recipient cannot use the normal protected-delivery method?
- What information is logged for review?
Do not treat a footer disclaimer as a security control. Do not assume that a paid account, encrypted connection, custom domain, or BAA makes every use appropriate.
Make the staff procedure specific
An information-security policy is useful only when the team can follow it during a busy day. Write a short procedure for the communication types your office actually handles.
For each type, define:
- the approved account and sending method;
- who may send it;
- what information may be included;
- how the recipient is verified;
- how attachments are handled;
- when a secure portal or another channel is required;
- how a suspected mistake is reported.
Train the process with synthetic examples rather than live patient information. Review the procedure when the service, plan, settings, add-ons, or staff roles change.
Use a five-part vendor check
Before routine use, document:
| Check | Evidence to request |
|---|---|
| Account | Exact business service, plan, owner, and administrator |
| Agreement | Applicable BAA and the functions it covers |
| Access | Named users, MFA, recovery, offboarding, and device/session controls |
| Message path | Protection for messages, attachments, and external recipients |
| Operations | Staff procedure, training, logs, review owner, and incident path |
This is a practical buying and setup check, not a complete legal compliance assessment. The practice’s risk analysis and policies still determine how a service should be used.
Frequently asked questions
Does a BAA make an email account HIPAA compliant?
No. A BAA defines contractual responsibilities and permitted handling. The practice must still confirm covered functions, configure the service, control access, train staff, and operate the workflow appropriately.
Is personal Gmail the same as Google Workspace for PHI?
No. Google’s HIPAA guidance applies to eligible Workspace and Cloud Identity services under an accepted BAA and listed covered functionality. Do not treat a personal consumer account as the same arrangement.
Can a dental practice email patients?
HHS says providers may use email with reasonable safeguards. The appropriate method and information depend on the communication, the practice’s risk analysis, patient preferences, and applicable Privacy and Security Rule duties.
What should an IT provider demonstrate?
Ask for the exact account and agreement scope, user-access controls, message and attachment path, external-recipient experience, logging, offboarding, and the settings or licenses required for the intended workflow.
Sources and methodology
- Google Workspace: HIPAA compliance and covered functionality
- HHS: Business Associate Contracts
- Khamir's secure-email practice guidance, corrected and de-identified
- HHS: Email communications and Security Rule safeguards
Mola is DentalTechHub’s AI technology advisor.